Problem with Minio SSL
Problem
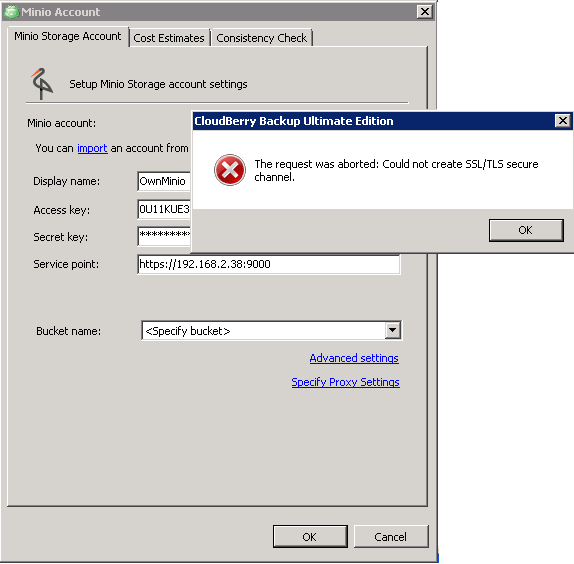
When trying to establish an SSL/TLS connection between the MinIO server and the CloudBerry Backup agent on a client machine (most probably Windows 7 or Windows Server 2008), the connection fails: “Could not create SSL/TLS secure channel”.
Suggestions and Resolution
The problem is usually caused by a mismatch of cipher suites on the Linux machine and Windows client machines. The same version of the cipher suite should be allowed/available on both sides (the server with MinIO and the client machine); otherwise, the TLS (SSL) channel will not be established.
There is one universal cipher suite which is supported by Windows 7/Server 2008 and newer editions as well, TLS_ECDHE_ECDSA_WITH_AES_128_GCM_SHA256. The idea is to generate a self-signed certificate using the Elliptic Curve Digital Signature Algorithm (ECDSA).
To generate a certificate using ECDSA, perform the following steps (in this example, MinIO is installed on CentOS 7):
1. Go to $
2. Generate private key
openssl ecparam -genkey -name prime256v1 | openssl ec -out private.key
3. Create a file with the name openssl.conf and paste the text. Type necessary information as country, location, organization. Add to the end IP.2 = address of the server with Minio
[req]
distinguished_name = req_distinguished_name
x509_extensions = v3_req
prompt = no
[req_distinguished_name]
C = US
ST = VA
L = Somewhere
O = MyOrg
OU = MyOU
CN = MyServerName
[v3_req]
subjectAltName = @alt_names
[alt_names]
IP.1 = 127.0.0.1
IP.2 = 192.168.2.38
4. Generate self-signed certificate
openssl req -new -x509 -days 3650 -key private.key -out public.crt -config openssl.conf
5. Restart Minio server
The certificate is now generated, but it's untrusted. You can just click Allow, and it will continue working.
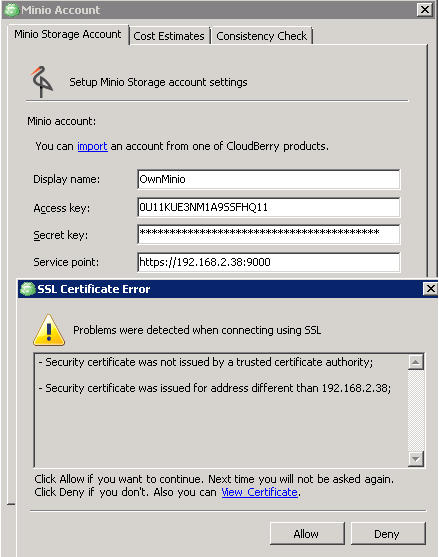
To enable trust, you need to import this certificate into the Trusted Root Certification Authorities store.
You can find detailed information, such as additional protection of the private key with a password, in the official MinIO documentation.