Situation
There is always a possibility that backup data could be modified or deleted from remote or local storage, either manually by an individual or by malware.
While any MSP should always be cautious about the possibility of intentionally or unintentionally harmful actions, it is good practice to set up proper security measures at the Management Console and Backup Agent levels.
Solution
Securing Backup Agent Application
To prevent the above-mentioned situations at Backup Agent level, make sure to protect the application with a master password, so that Backup Agent cannot be accessed by unauthorized persons to tamper with backup/restore plans or overall settings of the application.
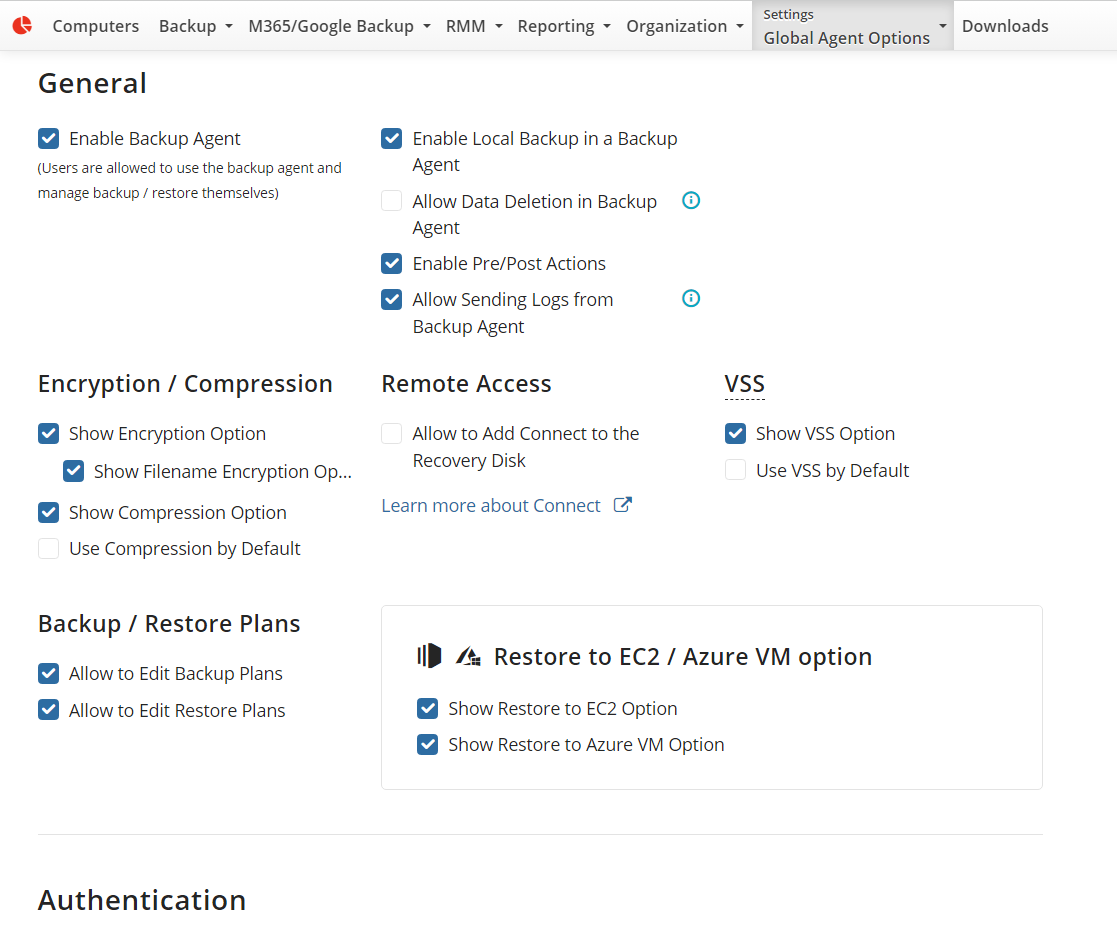
Furthermore, consider whether end users actually need the ability to remove data using the Backup Storage tab of Backup Agent. This ability can be revoked in the Management Console > Settings > Global Agent Options > Backup > Enable Data Deletion in Backup Agent:
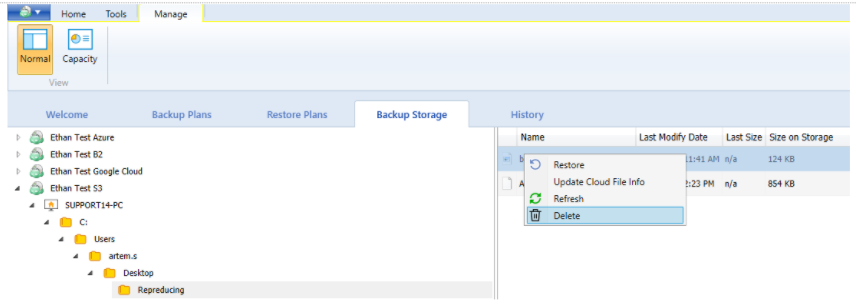
This way, you can ensure that the Backup Storage tab cannot be abused for unauthorized data removal:
Securing Management Console
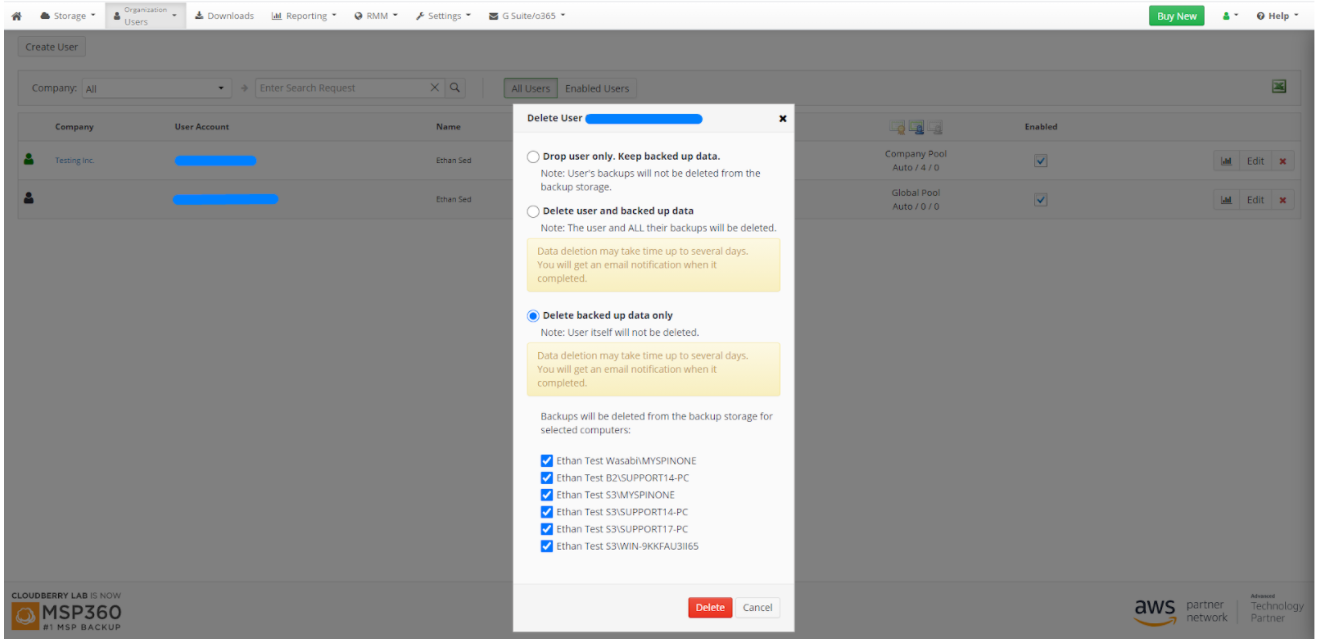
To improve the security of the Management Console, use two-factor authentication for your MSP account as well as for each of your sub-administrators. With that measure in place, data removal through the Management Console > Organization > Users cannot be abused:
The 3-2-1 backup storage strategy is a cornerstone of safe backup data storage. By complying with that strategy, you ensure that your backup operations will be properly secured from human error as well as internal and external threats even in case of issues with one of the backup storage accounts.
You can also restrict access to the Management Console based on the IP address used.
Additionally, make sure to comply with recognized security best practices: