Assuming IAM Role
Situation
Due to specific security considerations, it is not possible to use an IAM user with appropriate permissions to access S3 using CloudBerry Explorer. An IAM role is required.
Solution
The following setup can be used to enable access to the IAM role while using an IAM user with minimum permissions to authorize in CloudBerry Explorer.
- Create the IAM user (in this case study, cloudberry_explorer), then attach the following policy to that user:
{
	"Version": "2012-10-17",
	"Statement": [
    	{
        	"Action": [
            	"sts:AssumeRole"
        	],
        	"Resource": [
            	"arn:aws:iam::01234567890:role/iamrole"
        	],
        	"Effect": "Allow",
        	"Sid": "AllowAssumeExplorerRole"
    	}
	]
}
Make sure to specify the correct ARN for the role.
- Confirm that arn:aws:iam::01234567890:role/iamrole has the appropriate permissions assigned. Below is a minimum set of permissions required to work with a specific bucket:
{
    "Version": "2012-10-17",
"Statement": [
{
"Effect": "Allow",
"Action": [
"s3:ListBucket",
"s3:GetBucketLocation",
"s3:ListBucketMultipartUploads"
],
"Resource": "arn:aws:s3:::bucketname",
"Condition": {}
},
{
"Effect": "Allow",
"Action": [
"s3:AbortMultipartUpload",
"s3:DeleteObject",
"s3:DeleteObjectVersion",
"s3:GetObject",
"s3:GetObjectAcl",
"s3:GetObjectVersion",
"s3:GetObjectVersionAcl",
"s3:PutObject",
"s3:PutObjectAcl",
"s3:PutObjectVersionAcl"
],
"Resource": "arn:aws:s3:::bucketname/*",
"Condition": {}
},
{
"Effect": "Allow",
"Action": "s3:ListAllMyBuckets",
"Resource": "*",
"Condition": {}
}
]
}
Instead of bucketname, specify the real target bucket name.
- Edit the trust relationship for the IAM role:
{
  "Version": "2012-10-17",
  "Statement": [
	{
  	"Effect": "Allow",
  	"Principal": {
    	"AWS": "arn:aws:iam::123456789012:user/cloudberry_explorer"
  	},
  	"Action": "sts:AssumeRole",
  	"Condition": {
    	"StringEquals": {
      	"sts:ExternalId": "12345"
    	}
  	}
	}
  ]
}
The sts:ExternalId field can have any value; 12345 is just an example. Make sure to use the same value in the next step.
- Use the secret and access keys of cloudberry_explorer IAM user to add the storage to the CloudBerry Explorer software. Then close the application and open the settings.list file with any editor.
- In the settings.list file, find the Settings xsi:type="S3Settings" string for your storage account, then add the following lines:
<AssumedRoleARN>arn:aws:iam::01234567890:role/iamrole</AssumedRoleARN> <AssumedRoleExternalId>12345</AssumedRoleExternalId>
Read also the related blog post: https://www.msp360.com/resources/blog/assuming-an-iam-role/
- Open CloudBerry Explorer. The storage should be visible.
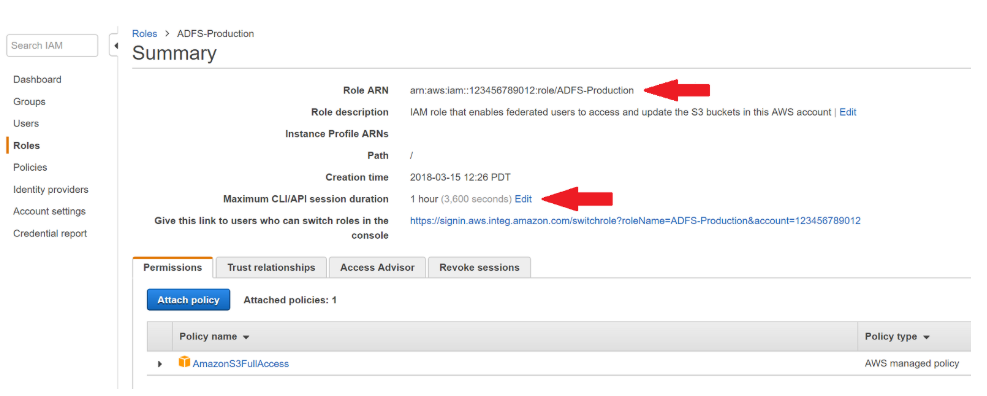
Note that the pre-signed URLs generated while using an IAM role will have a standard duration of 1 hour. The maximum possible duration is 12 hours.