How To Create IAM Role With Permissions Required For MBS
IAM roles are entities in AWS that allow you to access and control services. Managed Backup needs several permissions to be able to communicate with your Amazon S3 account. These permissions can be granted via an IAM role.
1. Preparations
If you’ve just started using Managed Backup Service, create a user and configure your storage account.
2. Adding the S3 storage in the MBS console
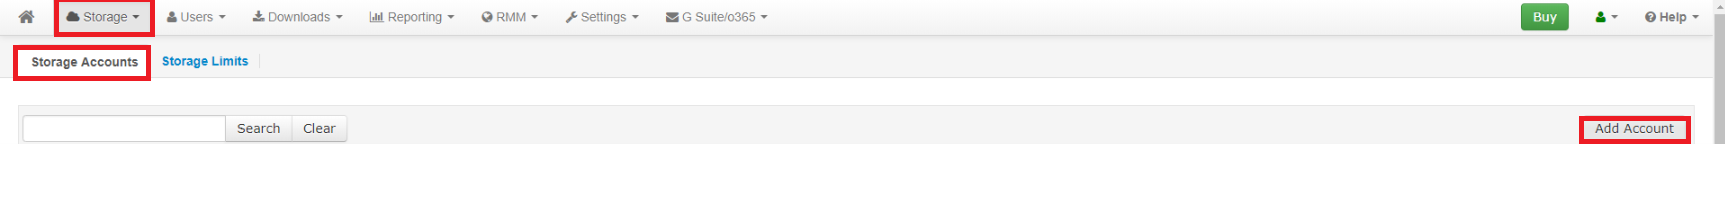
Log in to the Management Console, then under the Storage account section, click Add Account.
In the pop-up window, select Amazon S3 Cloud Storage and proceed with configuring your account.
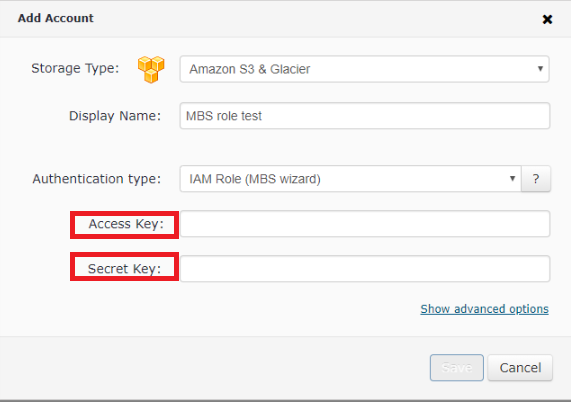
Having specified the storage account name in the Display Name field, click the “question” button to open a help window on MBS role policies.
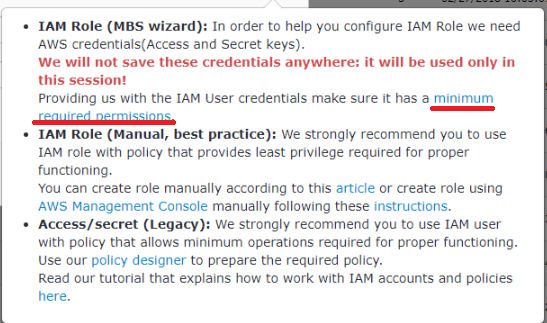
Click the minimum required permissions link to see the policy.
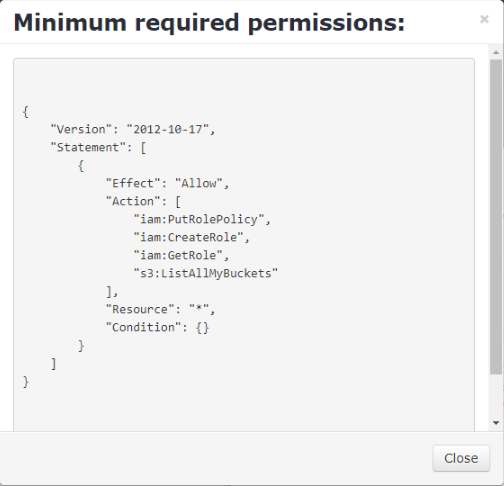
Do not close this window; you will need it soon. We will come back to this later to finish the configuration. Open a new tab in the browser to continue creating the user’s policy.
3. Creating and attaching the policy to an IAM user in the AWS console
The next step is to go to your AWS account and attach the policy to the user you are going to use for the backup. Log in to your AWS account and go to the IAM (Identity and Access Management) section.
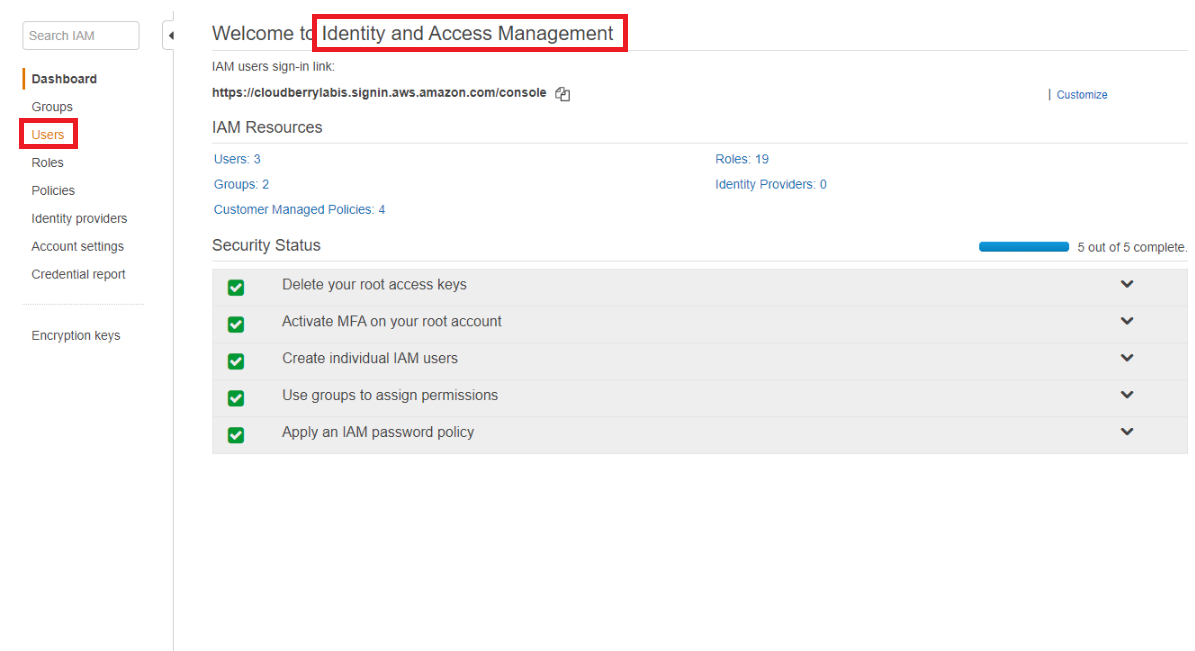
Choose the needed user.
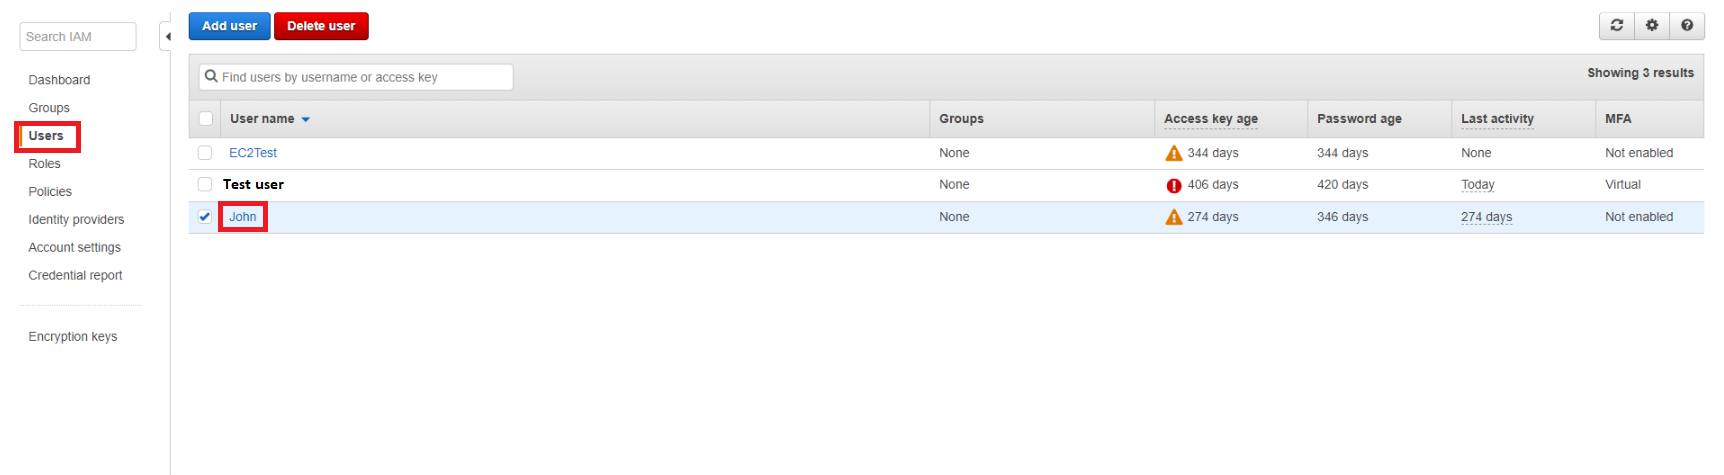
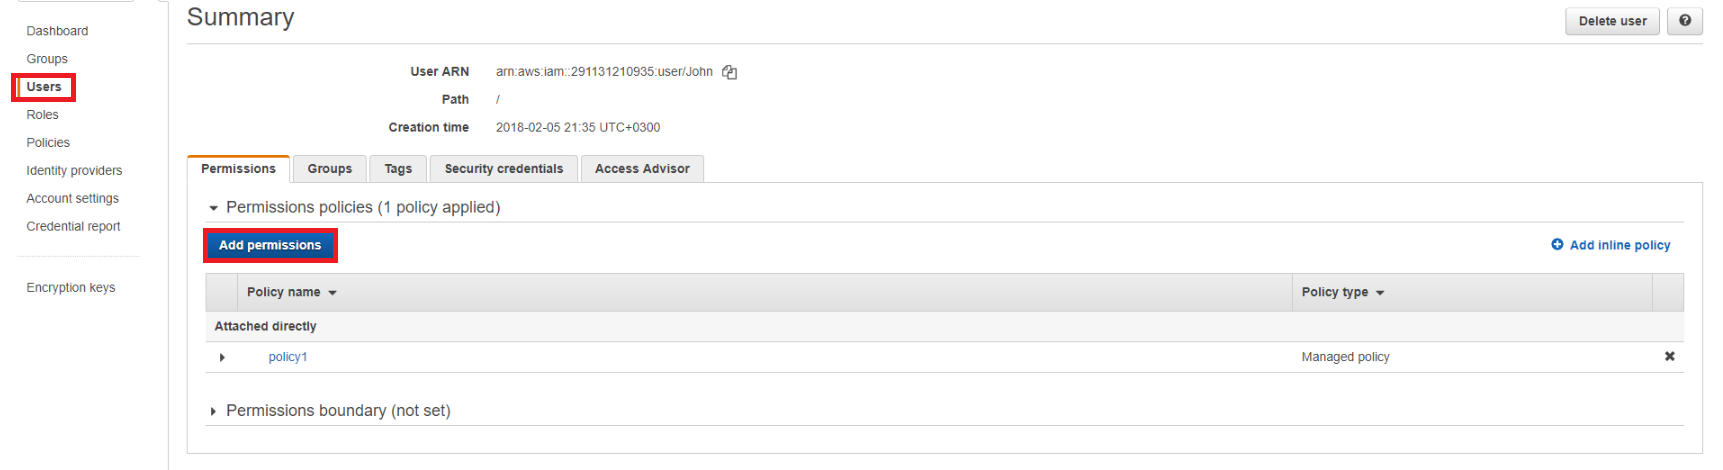
Click the user to start editing the settings. The blue Add permissions button will open a window where you can create a new policy for that user.
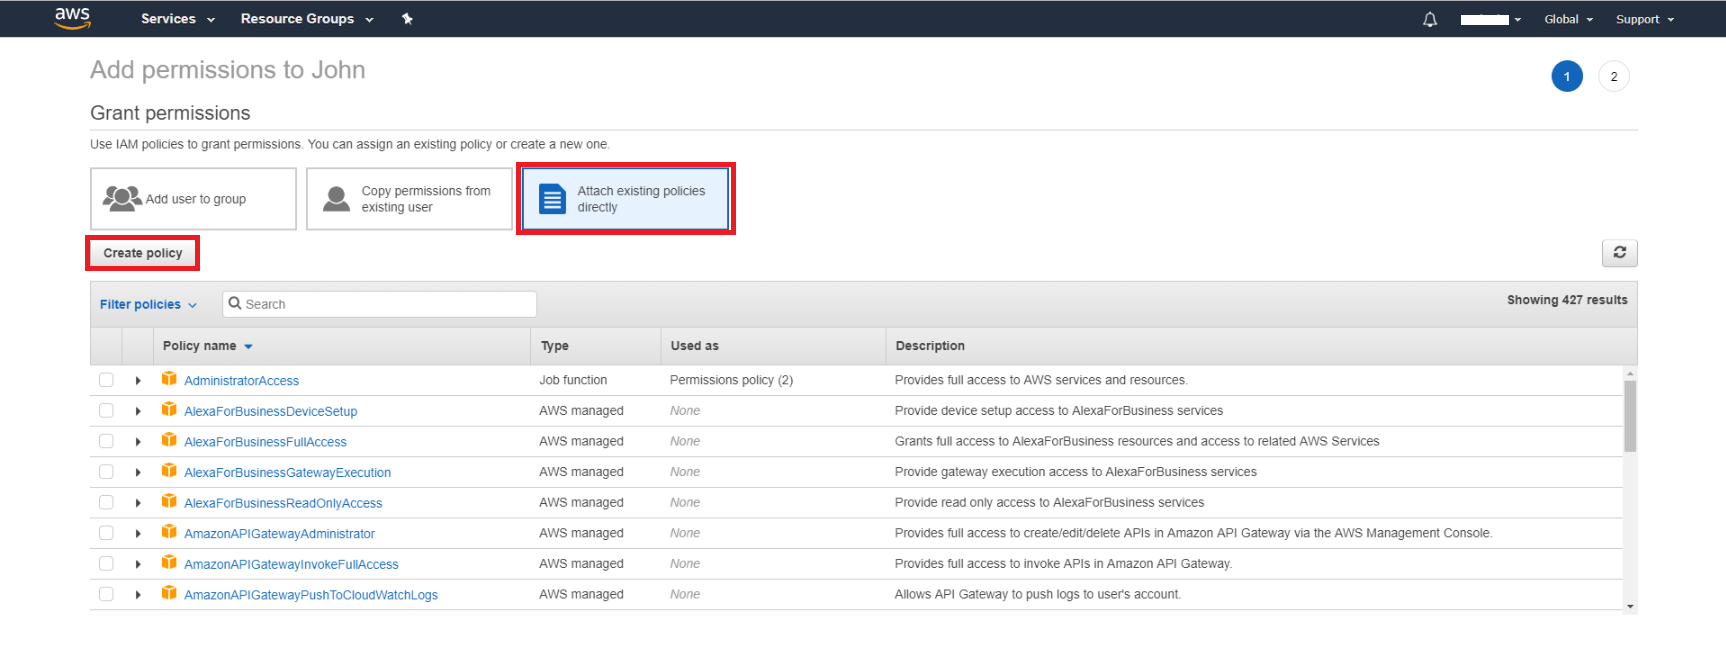
By selecting Attach existing policies directly you get a list of predefined policies. Click the “Create policy” button to create a new one that will be attached to this user for the Managed Backup Service.
In the Create policy window, switch to the JSON format. You will see a default policy.
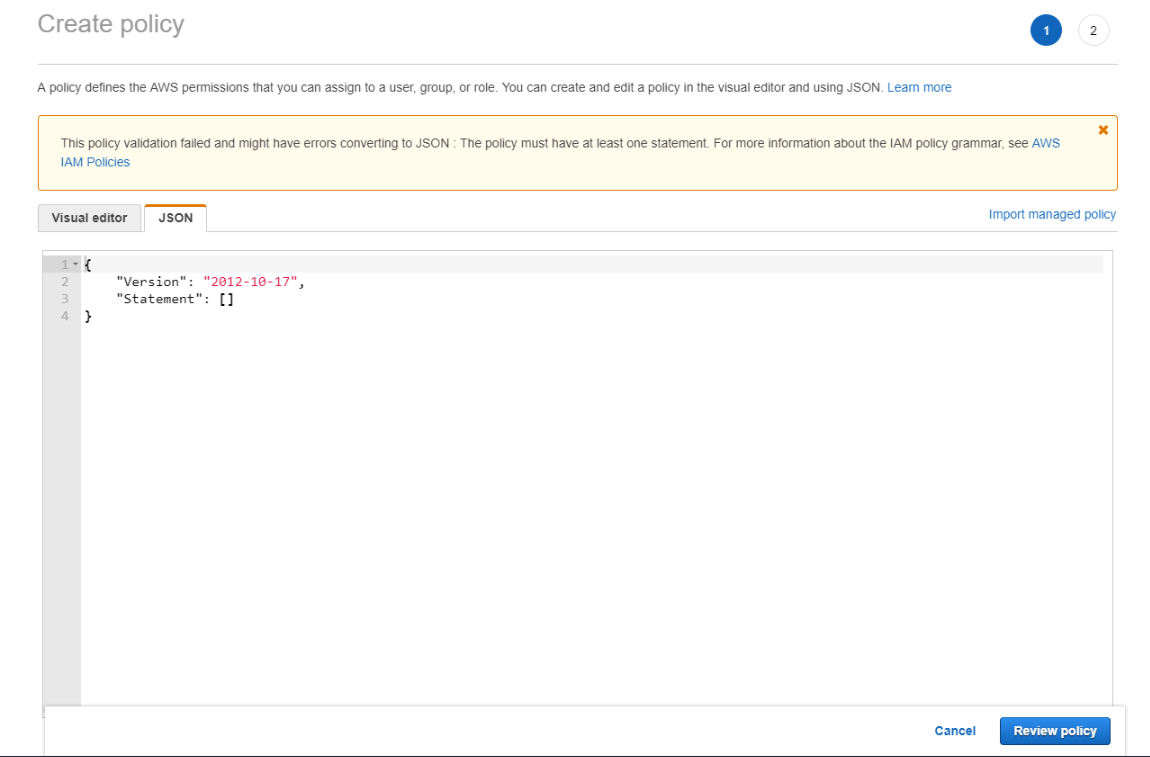
Now you need to go back to the Management Console and copy the permissions from step 2 and replace the default ones in the AWS account.
{
    "Version": "2012-10-17",
    "Statement": [
        {
            "Effect": "Allow",
            "Action": [
                "iam:PutRolePolicy",
                "iam:CreateRole",
                "iam:GetRole",
                "s3:ListAllMyBuckets"
            ],
            "Resource": "*",
            "Condition": {}
        }
    ]
}
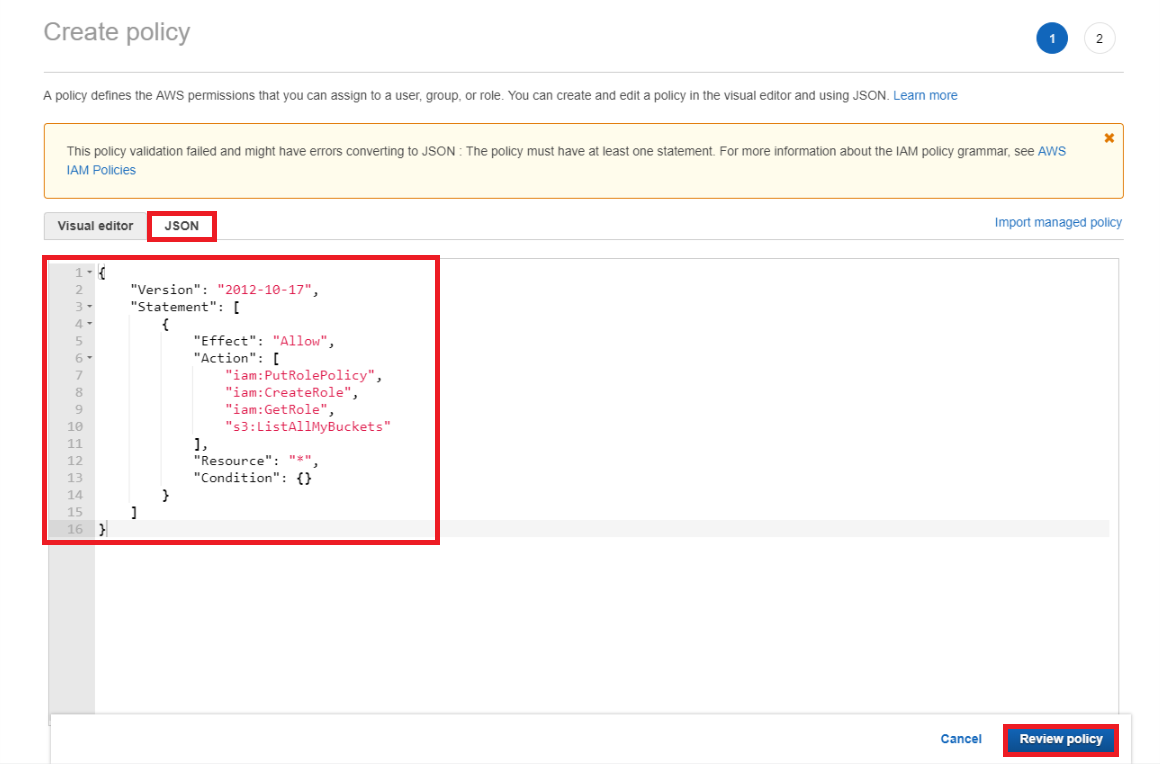
Now, click the Preview policy button.
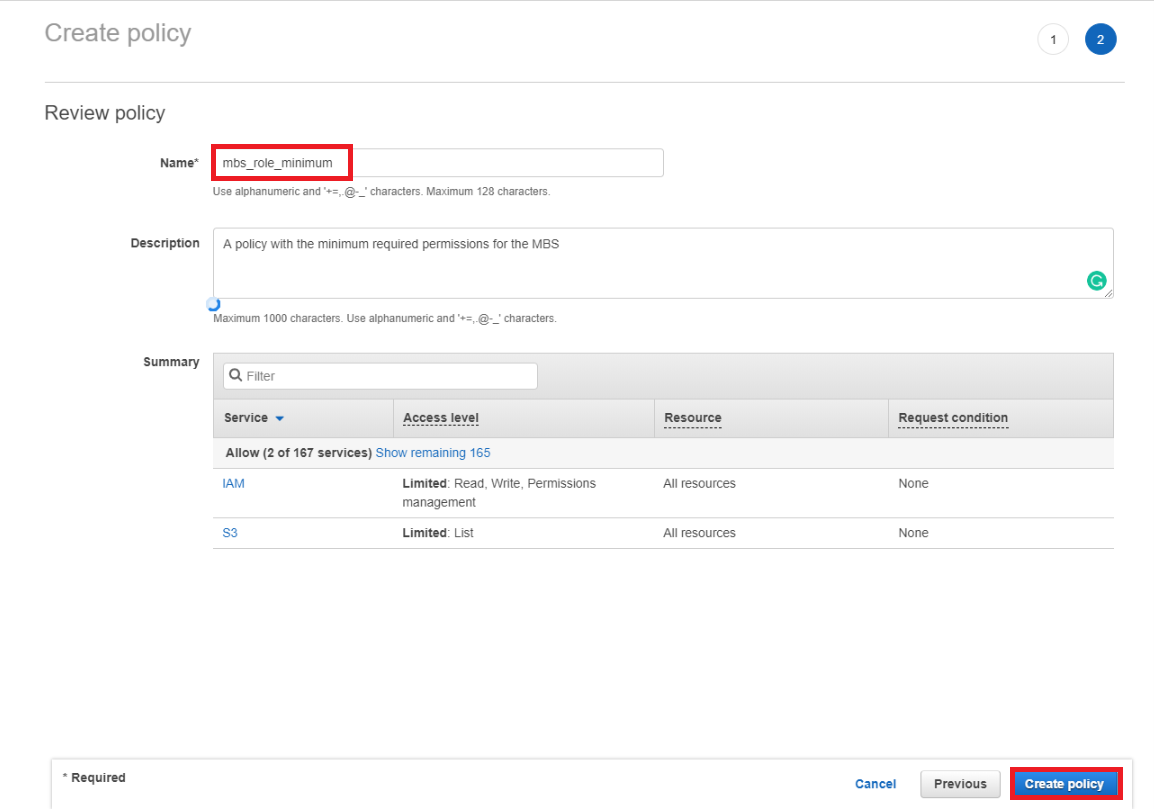
Give your policy a name and click the Create policy button. Comments in the Description field are optional. If everything was done correctly, you will see a message that your policy has been created.
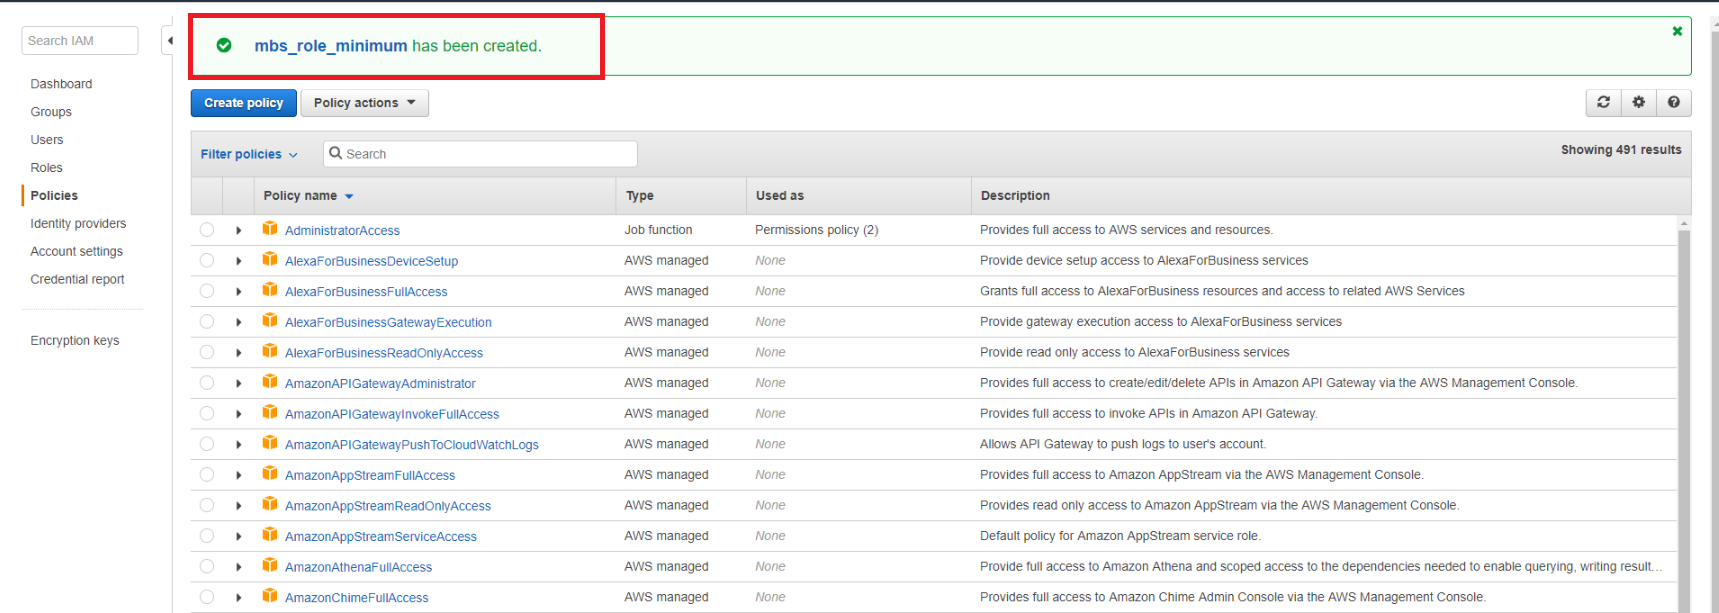
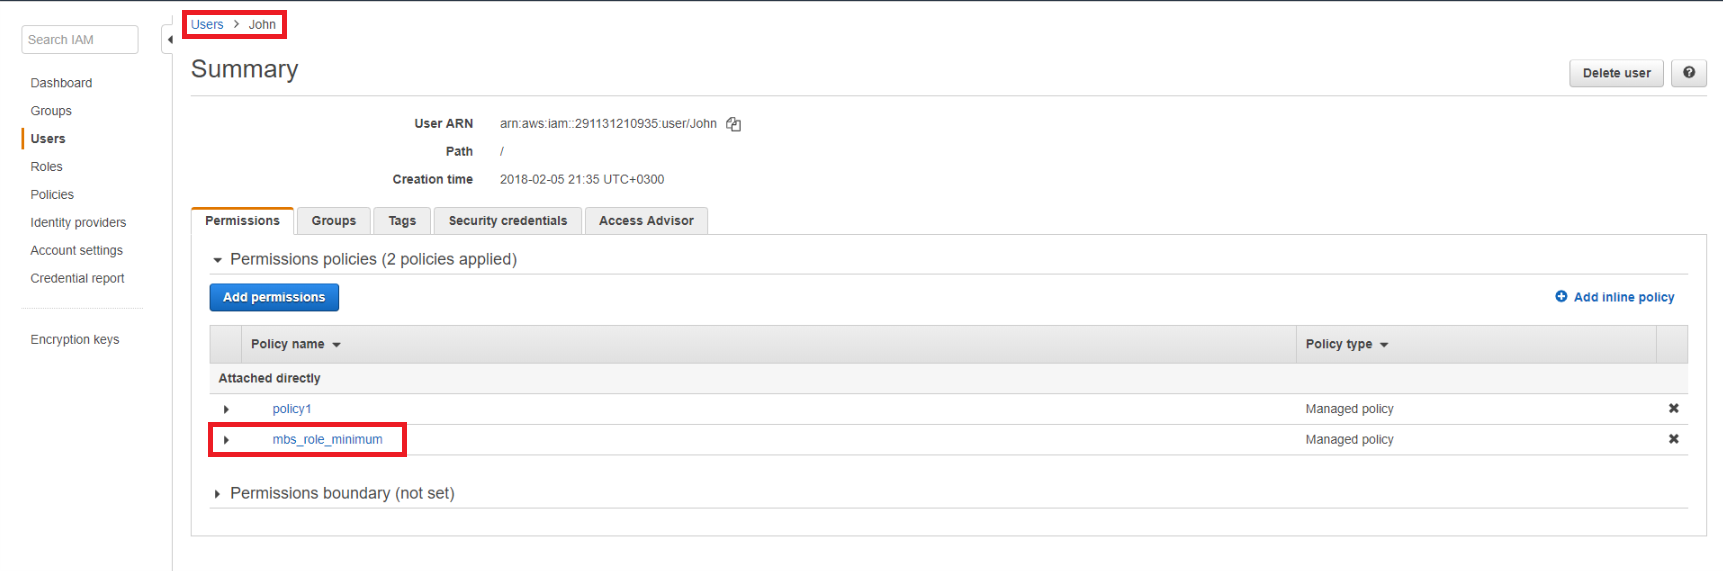
You can go back to the Users tab and attach this policy to your user. Some browsers may open a new tab to create a new policy in the AWS account. Check whether you have the Users tab open and close the one with the policy creation. If you have done everything correctly, you will have the following tab opened.
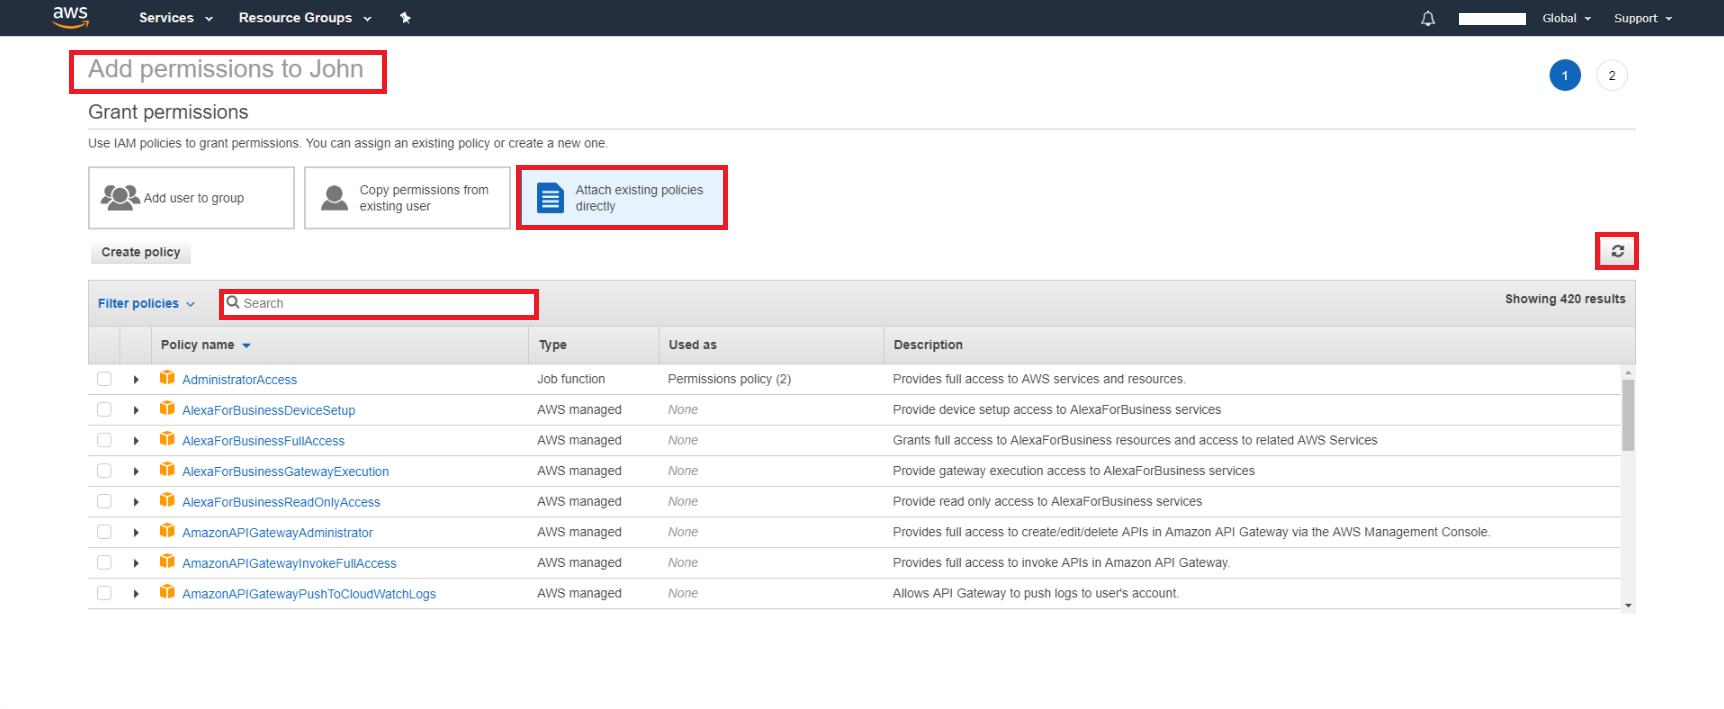
This time, all you need to do is refresh the list of policies and type your policy’s name in the search field.
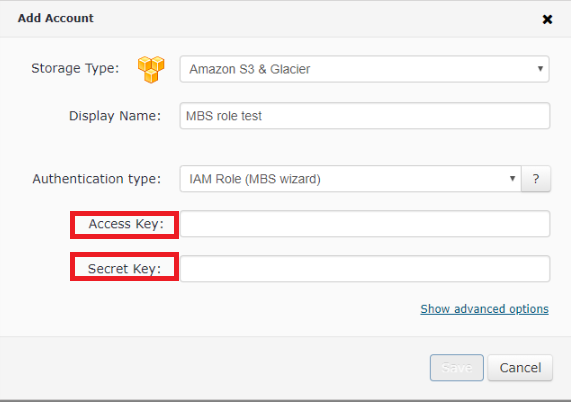
Switch to the Management Console, where you have the pop-up window with the storage account settings open, and specify the proper Access Key and a Secret Key of the IAM User with the policy. You might need to click the “question” button again to make the help pop-up window disappear.
Once the credentials are entered, click the Save button and proceed with selecting a Destination bucket for your backups. You can choose an existing bucket or create a new one.
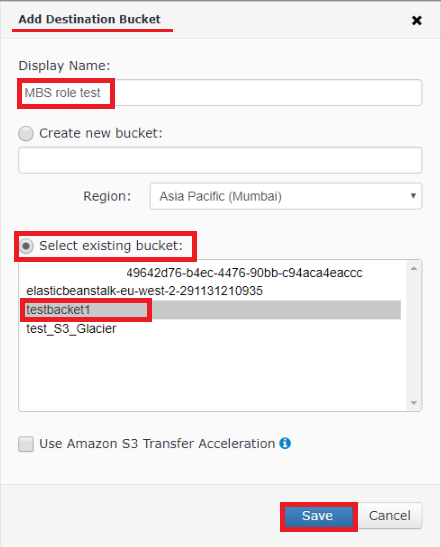
Once you have specified a Destination bucket, you can add this destination to all your existing Managed Backup users or only to some of them.
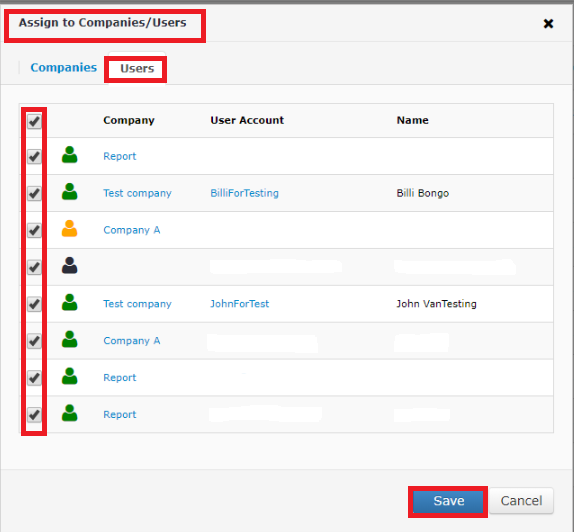
Now you are ready to start your first backup job.
Feel free to contact us should you need any assistance.
Contact Us
- Tech questions
- Sales questions: sales@msp360.com